39 antivirus inspection is proxy based palo alto
How to Configure SSL Decryption - Palo Alto Networks SSL (Secure Sockets Layer) is a security protocol that encrypts data to help keep information secure while on the internet. SSL certificates have a key pair: public and private, which work together to establish a connection. PAN-OS can decrypt and inspect SSL inbound and outbound connections going through the firewall. Threat Assessment: BlackCat Ransomware - Unit42 BlackCat (aka ALPHV) is a ransomware family that surfaced in mid-November 2021 and quickly gained notoriety for its sophistication and innovation. Operating a ransomware-as-a-service (RaaS) business model, BlackCat was observed soliciting for affiliates in known cybercrime forums, offering to allow affiliates to leverage the ransomware and keep ...
Palo Alto: PSE: Foundation Accreditation Exam Answer - Blogger How is Palo Alto Networks driving the next evolution in the industry? ... Antivirus inspection is proxy-based. false. Which two capabilities are provided by the Panorama or firewall ACC? (Choose two.) accounting information about licenses associated with applications. information about applications themselves and the traffic used by the ...

Antivirus inspection is proxy based palo alto
Decrypt Traffic for Full Visibility and Threat ... - Palo Alto Networks Configure the SSL Decryption SSL Forward Proxy settings to block exceptions during TLS negotiation and block sessions that can't be decrypted: Block sessions if resources not available prevents allowing potentially dangerous connections but may affect the user experience. Configure the SSL Decryption SSL Protocol Settings Endpoint Protection - Palo Alto Networks Endpoint Protection - Palo Alto Networks Proven Endpoint Protection Safeguard your endpoints with best-in-class NGAV, device control, disk encryption and host firewall. Get the guide WHY IT MATTERS To secure what's next, you need AI-powered security that's continually learning. You face endless hurdles in your pursuit to secure your endpoints. Palo Alto Next-Generation Firewall Features | Palo Alto Networks Firewalls Palo Alto Networks next-generation firewalls arm you with a two-pronged approach to stopping these attacks. Unwanted applications are blocked through App-ID, and the applications you choose to allow through are scanned for vulnerability exploits by our NSS-approved IPS engine. Enable full IPS protection while maintaining performance.
Antivirus inspection is proxy based palo alto. Palo Alto SSL Decryption - Network Interview Configuration of SSH Proxy Step 1. Configure interfaces as either virtual wire, Layer 2, or Layer 3 interfaces. Decryption can be performed on virtual wire, Layer 2, or Layer 3 interfaces of firewall. Step 2. Create a decryption policy rule for SSH proxy to define traffic for the firewall. Step3. Commit the configuration. SSL Inbound Inspection Decrypt Traffic for Full Visibility and Threat Inspection Configure the SSL Decryption SSL Forward Proxy settings to block exceptions during SSL negotiation and block sessions that can't be decrypted: Block sessions if resources not available prevents allowing potentially dangerous connections but may affect the user experience. Configure the SSL Decryption SSL Protocol Settings Content-ID: High-Performance Threat Prevention - Palo Alto Networks Content-ID gives you a real-time threat prevention engine, combined with a comprehensive URL database, and elements of application identification to: Limit unauthorised data and file transfers. Detect and block exploits, malware and malware communications. Control unapproved web surfing. Set Up Antivirus, Anti-Spyware, and Vulnerability ... - Palo Alto Networks Configure the Palo Alto Networks Terminal Server (TS) Agent for User Mapping ... Migrate Port-Based to App-ID Based Security Policy Rules. Rule Cloning Migration Use Case: Web Browsing and SSL Traffic. ... Set Up Antivirus, Anti-Spyware, and Vulnerability Protection. DNS Security. About DNS Security.
The Evolution of Firewalls - Palo Alto Networks A firewall was defined as a tool for monitoring and controlling the flow of data traffic in and out of a network based on a set of filtering rules applied to data packets. While it might have been appropriate at the time, this primitive tool was totally reactive . As networks have evolved, so too have firewalls which have now become more proactive. Best Practices for Ransomware Prevention - Palo Alto Networks The Anti-Virus and Wildfire content contains a list of domains Palo Alto Networks has identified as being potentially associated with malicious traffic; network administrators can block DNS requests to these domains with this profile, or choose to sinkhole the traffic to an internal IP address they have configured for further analysis. Advanced Threat Prevention Deployment - Palo Alto Networks Palo Alto Networks' next-generation Firewall offers Application Identification, URL Filtering, Vulnerability Protection, Antivirus, Anti-Spyware, WildFire and DoS Protection technologies capable of detecting and preventing a vast range of threats and malicious communications over the network. Additionally each of these technologies Set Up Antivirus, Anti-Spyware, and Vulnerability ... - Palo Alto Networks Configure the Palo Alto Networks Terminal Server (TS) Agent for User Mapping ... Migrate Port-Based to App-ID Based Security Policy Rules. Rule Cloning Migration Use Case: Web Browsing and SSL Traffic. ... Set Up Antivirus, Anti-Spyware, and Vulnerability Protection. DNS Security. About DNS Security.
Antivirus Config FortiOS 7.0 Profile Based ?? : fortinet - reddit In flow you could do basic flow inspection whereas in proxy you could do full proxy inspection OR flow inspection depending on the need. In 6.2 and afterwards firewall policies where redesigned (enhanced) to be defined in a format called profile or policy based (same like Palo Alto firewalls). PDF Moving From Detection to Prevention of Modern Malware - Palo Alto Networks designed to detect malware. Other network-based anti-malware solutions are proxy-based, which are typically prohibitively slow and limited to only protecting against web-based malware. However, antivirus web-proxies, IPS products and email gateway products share a far more serious and fundamental flaw - PDF Integrated Threat Prevention - Palo Alto Networks drawback of network antivirus offerings that rely on proxy-based scanning engines. Proxy-based network antivirus solutions have historically lacked the performance capacity to be widely deployed in a real-time environment (e.g., web applications) because they pull the entire file into memory before the scanning process began. Palo Alto - SSL Inbound Inspection Webserver - Faatech Policies > Decryption > Add Give the policy a clear name. Choose the zone that's your external side. Source address should be left to any. Choose the zone where your webserver resides in. Enter the public IP (pre-NAT IP) of your webserver and NOT the internal IP address of the webserver. Select service-https (443/tcp) as the service.
Palo Alto Networks: 10 Must haves for Detection and Response ...
How to Implement and Test SSL Decryption - Palo Alto Networks There will be no certificate errors, as the connection is not being proxied—just inspected. Examine the logs for this inbound connection. The applications will not be "ssl" but the actual applications found inside the SSL tunnel. Click the magnifying glass icon in those log entries to confirm decrypted connections. Helpful CLI Commands

Group Update Provider for CSI Antivirus | PO Tools
Next-Generation Firewall Solutions - Palo Alto Networks Reactive security can't keep up with today's threats — or prepare you for tomorrow's. We've changed the game by making network security intelligent and proactive. Driven by innovation, our award-winning security features the world's first ML-Powered NGFW and empowers you to stay ahead. Read the eBook. Of Fortune 100. 95%. In network ...

PALO ALTO NETWORK: Palo Alto - Antivirus Profile
Network-based Malware Protection | Palo Alto Networks Palo Alto Networks next-generation firewalls allow organizations to first block unwanted applications with App-ID and then scan the allowed applications for malware. Broad-based protection against a range of malware. The antivirus engine detects and blocks viruses, spyware phone home, spyware download, botnet, worms and trojans.
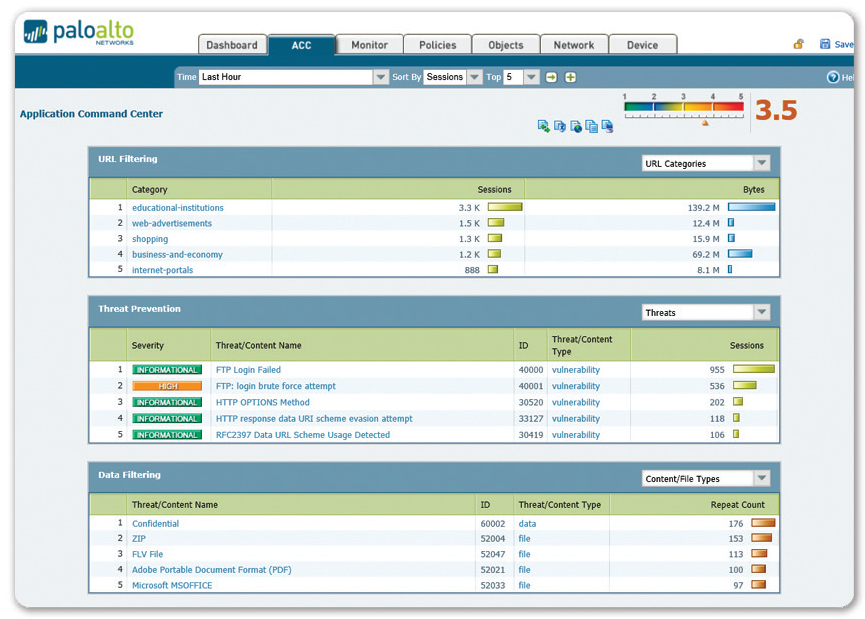
Palo Alto Networks Enterprise Firewall PA-200 | PaloGuard.com.au
Objects > Security Profiles > Antivirus - Palo Alto Networks Device > Certificate Management > SSL Decryption Exclusion Device > Response Pages Device > Log Settings Select Log Forwarding Destinations Define Alarm Settings Clear Logs Device > Server Profiles Device > Server Profiles > SNMP Trap Device > Server Profiles > Syslog Device > Server Profiles > Email Device > Server Profiles > HTTP

Palo Alto: CNSE -Palo Alto - Firewall configuration essentials
Configuring Palo Alto for SSLI and VPN - SecureW2 Configure Palo Alto for SSL Inspection. Import the intermediate CA for SSL Decryption to Palo Alto. ... The best way to configure your Managed Devices for certificate-based network authentication, is a combination of: ... Select Type as SSL Forward Proxy. Optional (Create Decryption Profile) Click OK to save the changes;

My Palo Alto Networks PCNSE Journal: Configuring Antivirus Blocking on ...
Cisco ASA Firewall Vs Palo Alto Firewall! (Table Comparison) The most unique feature of Alto Palo is Automatic Verdict, which can recognize any threat range. It sends out immediate alerts to all subscribers who have access during a security breach. Main Differences Between Cisco Firewall and Palo Alto NGFW. 1. Cisco Firewall includes a web-based access GUI, but Palo Alto does not have a web-based access ...
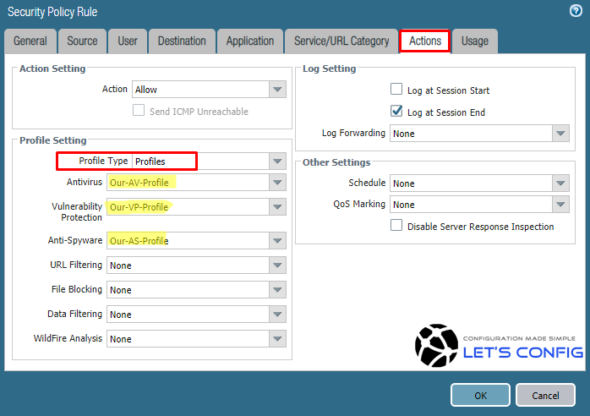
Set Up Antivirus, Anti-Spyware, and Vulnerability Protection on Palo Alto
Palo Alto Networks - Network-based Malware Protection - NextGig Systems Call 1-805-277-2400 Broad-based protection against a range of malware. The antivirus engine detects and blocks viruses, spyware phone home, spyware download, known Bots, as well as worms and Trojans. Additional features, over and above the protection against a wide range of threats, include:
0 Response to "39 antivirus inspection is proxy based palo alto"
Post a Comment